BGP FlowSpec DDoS mitigation on your edge routers
IP Infusion delivers DDoS mitigation on the routers at your edge: OcNOS-SP samples traffic with sFlow, takes BGP FlowSpec and RTBH rules from a FastNetMon detector, and drops or rate-limits the attack in hardware within two seconds, without rerouting traffic to a scrubbing center.
How the edge router stops an attack
The edge router sends sFlow samples to FastNetMon. When traffic to a host crosses a configured threshold, FastNetMon sends a mitigation rule to the router over BGP, and the router enforces it in hardware. The rule can match only the attack flow, or everything sent to the host.
The same attack, two ways to stop it
FlowSpec drops only the attack flow. The rule matches the attack, and the router discards or rate-limits it in hardware while other traffic to the host keeps flowing.
RTBH drops everything sent to the target. The route points the host at a null next-hop, so every packet for it is dropped, legitimate traffic included, which protects your links from saturation. The host stays unreachable until the route is withdrawn.
Illustrative.
Tested with FastNetMon, step by step
The IP Infusion deployment guide was tested on OcNOS 7.0.0 with FastNetMon 2.0.367 and later. It covers the sFlow export, the BGP session, FlowSpec and RTBH, thresholds, and failover.
FastNetMon runs as a virtual machine and is supported by FastNetMon. If it stops, the BGP session times out and the router withdraws its rules, so traffic returns to its normal path.
Get the deployment guide →What the edge router enforces
All 26 OcNOS-SP platforms support BGP FlowSpec and RTBH, and the router adds its own protections.
| Capability | What it does | Where |
|---|---|---|
| BGP FlowSpec | Takes filter rules from the detector over BGP and installs them in hardware. The action is discard or rate-limit. | All OcNOS-SP |
| FlowSpec per VRF | Separate FlowSpec policies for each tenant VRF | All OcNOS-SP |
| RTBH | Routes from the detector point the target at a null next-hop, with the IANA BLACKHOLE community | All OcNOS-SP |
| sFlow | Samples ingress traffic at a configured rate and sends it to the collector in-band | All OcNOS-SP |
| IPFIX | Flow export as an alternative to sFlow | OcNOS-SP |
| uRPF, strict and loose | Drops packets with spoofed source addresses | All OcNOS-SP |
| Hardware ACLs | Match on addresses, protocol, ports, TCP flags, DSCP and fragments, with timed rules | All OcNOS-SP |
| Control plane policing | Configurable CoPP protects the router’s own CPU | Selected platforms |
| Fail-safe | If the detector stops, the BGP session times out after its hold timer and the router withdraws its rules | All OcNOS-SP |
One hardware-profile command offloads FlowSpec rules to the ASIC. As of OcNOS 7.0, FlowSpec supports IPv4; use RTBH for IPv6 attacks. Support varies by platform: check the OcNOS Feature Matrix.
Detection-to-mitigation in seconds.
The architecture brief and the deployment app note: the high-level picture plus the step-by-step configuration for BGP Flowspec and RTBH on OcNOS with FastNetMon.
BGP FlowSpec DDoS Mitigation: OcNOS + FastNetMon
How OcNOS-SP edge routers and FastNetMon detect and stop DDoS attacks with BGP FlowSpec and RTBH, within two seconds.
Get the briefAutomated DDoS Mitigation: Deployment Guide
Step-by-step configuration: BGP Flowspec policies, RTBH triggering, FastNetMon integration with OcNOS, the ready-to-deploy reference.
Get the app noteEdge routers that enforce it
BGP FlowSpec and RTBH are supported on all 26 OcNOS-SP platforms. Pick the router by the edge it protects.
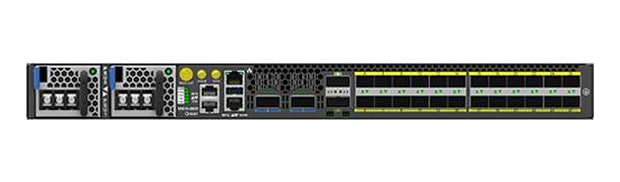
Aggregation edge
UfiSpace S9510-28DC
Qumran 2A · 800 Gbps
24 × 25G, 2 × 100G, 2 × 400G
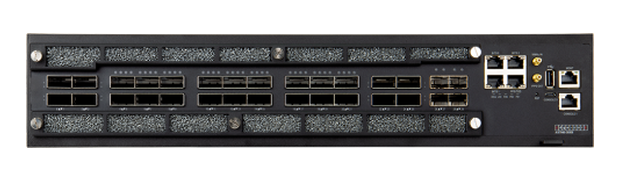
Metro and core
Edgecore AS7946-30XB (AGR400)
Qumran 2C · 2.4 Tbps
4 × 25G, 22 × 100G, 4 × 400G
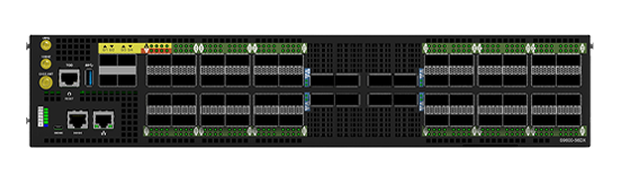
Metro edge
UfiSpace S9600-56DX
Qumran 2C · 4.8 Tbps
4 × 25G, 48 × 100G, 8 × 400G
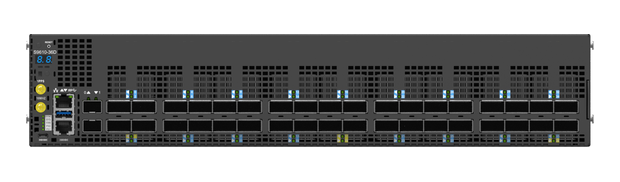
Peering and transit edge
UfiSpace S9610-36D
Jericho2C+ · 14.4 Tbps
36 × 400G
Every model on the OcNOS Hardware Compatibility List with OcNOS-SP can enforce FlowSpec and RTBH.
DDoS mitigation with OcNOS: FAQ
Plan DDoS mitigation for your edge.
We map your peering and transit edge, the FlowSpec and RTBH policy, and the OcNOS-SP routers that enforce it.
BGP FlowSpec DDoS Mitigation: OcNOS + FastNetMon
Quick form. Your PDF will download immediately after submit.
✓ Opening your PDF in a new tab…
If it didn't open, use the link below.
Automated DDoS Mitigation: OcNOS + FastNetMon Deployment Guide
Quick form. Your PDF will download immediately after submit.
✓ Opening your PDF in a new tab…
If it didn't open, use the link below.