Part of IP Infusion's guide to Segment Routing.
Scaling IS-IS Segment Routing to nationwide or global service provider networks requires partitioning the network into multiple IGP domains. Each IS-IS domain operates independently with its own SRGB and topology. BGP Labeled Unicast (BGP-LU) stitches these SR domains together at the ASBR (Autonomous System Border Router) level, enabling end-to-end EVPN services without requiring a single flat IS-IS domain or full-mesh BGP between all PEs.
Multi-Domain Architecture
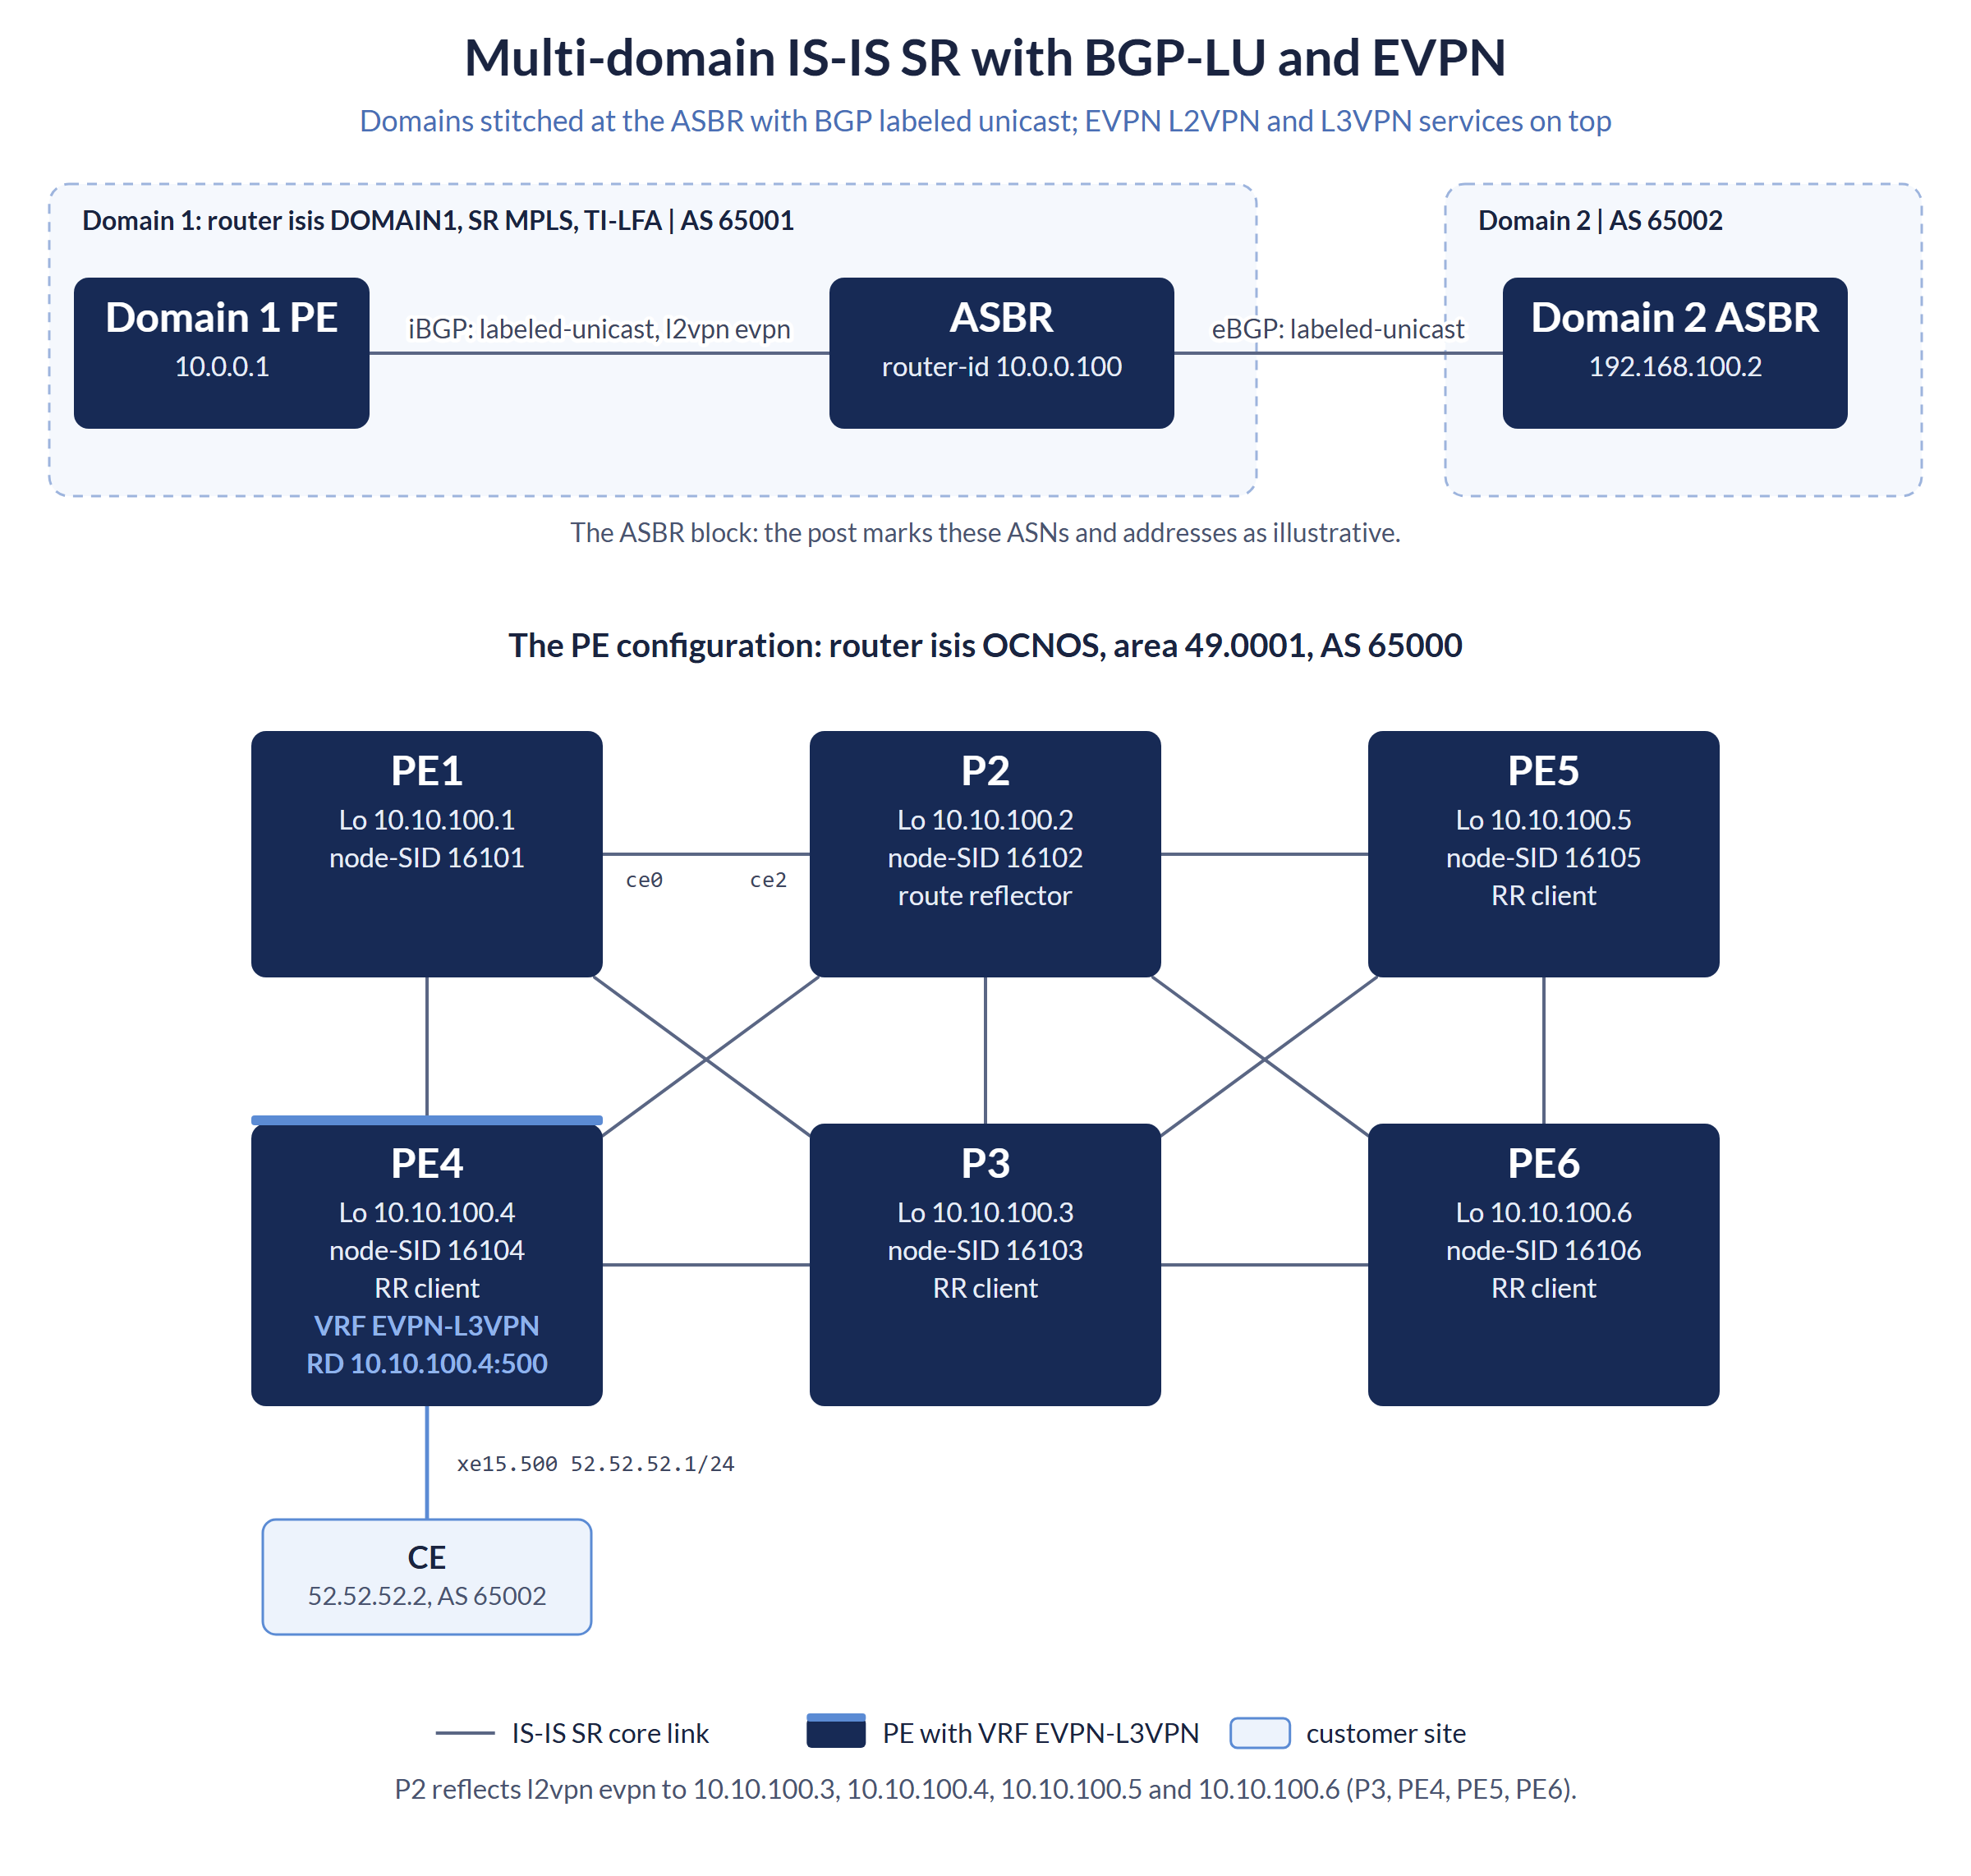
BGP-LU: Stitching SR Domains
BGP Labeled Unicast distributes MPLS-labeled IPv4/IPv6 prefixes (loopback addresses) between SR domains. The ASBR:
- Receives the SR label for a PE loopback from Domain 1's IS-IS
- Re-originates it into Domain 2 with a new BGP-allocated label
- Programs its forwarding table to swap the incoming label to the outgoing SR label
This allows PE1 in Domain 1 to reach PE2 in Domain 2 using a two-label stack: the BGP-LU label (outer) and the EVPN service label (inner).
ASBR Configuration: BGP-LU Label Stitching
! OcNOS ASBR: BGP-LU label stitching between two IS-IS SR domains
! ASNs and addresses below are illustrative; adapt them to your deployment.
!
! Step 1: IS-IS Segment Routing in the domain
router isis DOMAIN1
 is-type level-2-only
 metric-style wide
 net 49.0001.0000.0000.0100.00
 dynamic-hostname
 fast-reroute ti-lfa level-2 proto ipv4
 segment-routing mpls
!
! Step 2: BGP Labeled Unicast to advertise loopbacks across the domain boundary
router bgp 65001
 bgp router-id 10.0.0.100
 !
 ! iBGP to Domain 1 PEs (EVPN control plane)
 neighbor 10.0.0.1 remote-as 65001
 neighbor 10.0.0.1 update-source loopback1
 !
 ! eBGP to the Domain 2 ASBR for BGP-LU
 neighbor 192.168.100.2 remote-as 65002
 !
 ! BGP Labeled Unicast address family (allocate and advertise SR loopback labels)
 address-family ipv4 labeled-unicast
  neighbor 10.0.0.1 activate
  neighbor 192.168.100.2 activate
 exit-address-family
 !
 ! EVPN sessions: PE-to-PE across domains
 address-family l2vpn evpn
  neighbor 10.0.0.1 activate
 exit-address-family
!
commitPE Configuration: EVPN Services Across Domains
! OcNOS PE: IS-IS Segment Routing + EVPN L2VPN/L3VPN
!
! Step 1: IS-IS Segment Routing underlay (PE1)
!   Prefix-SID is configured on the loopback, NOT under router isis
interface loopback1
 ip address 10.10.100.1/32
 prefix-sid index 101
!
interface ce0
 description To-P2-ce2
 load-interval 30
 ip address 10.66.12.1/24
 mtu 9216
 label-switching
 isis network point-to-point
 isis circuit-type level-2-only
 ip router isis OCNOS
 no isis hello padding
!
router isis OCNOS
 is-type level-2-only
 metric-style wide
 mpls traffic-eng router-id 10.10.100.1
 mpls traffic-eng level-2
 capability cspf
 dynamic-hostname
 fast-reroute ti-lfa level-2 proto ipv4
 net 49.0001.0000.0000.0001.00
 passive-interface loopback1
 segment-routing mpls
!
! Step 2: MP-BGP EVPN route reflector (P2)
router bgp 65000
 bgp router-id 10.10.100.2
 no bgp inbound-route-filter
 neighbor EVPN-RRC peer-group
 neighbor EVPN-RRC remote-as 65000
 neighbor EVPN-RRC update-source loopback1
 neighbor 10.10.100.3 peer-group EVPN-RRC
 neighbor 10.10.100.4 peer-group EVPN-RRC
 neighbor 10.10.100.5 peer-group EVPN-RRC
 neighbor 10.10.100.6 peer-group EVPN-RRC
 !
 address-family l2vpn evpn
  neighbor EVPN-RRC activate
  neighbor EVPN-RRC route-reflector-client
 exit-address-family
!
! Step 3: EVPN MPLS, IRB and VTEP global IP (PE4)
evpn mpls enable
!
evpn mpls irb
!
evpn mpls vtep-ip-global 10.10.100.4
!
! Step 4: IP VRF with L3VNI for the L3VPN service (PE4)
ip vrf EVPN-L3VPN
 rd 10.10.100.4:500
 route-target both 500:500
 l3vni 5000
!
! Step 5: Access sub-interface bound to the VRF (PE4)
interface xe15
 mtu 9216
!
interface xe15.500
 encapsulation dot1q 500
 ip vrf forwarding EVPN-L3VPN
 ip address 52.52.52.1/24
 mtu 9216
!
! Step 6: MP-BGP on the PE: EVPN family + per-VRF IPv4 family (PE4)
!   VRF address family is the flat "address-family ipv4 vrf <NAME>" form
router bgp 65000
 bgp router-id 10.10.100.4
 neighbor 10.10.100.2 remote-as 65000
 neighbor 10.10.100.2 update-source loopback1
 !
 address-family l2vpn evpn
  neighbor 10.10.100.2 activate
 exit-address-family
 !
 address-family ipv4 vrf EVPN-L3VPN
  redistribute connected
  neighbor 52.52.52.2 remote-as 65002
  neighbor 52.52.52.2 activate
 exit-address-family
!
commit
Verification Commands
! OcNOS verification commands
!
! IS-IS SR topology, metrics and next-hops (PE1):
show isis topology
!
! MPLS SR label forwarding table / FTN entries (PE1):
show mpls forwarding-table
!
! MPLS incoming label map / ILM entries on a transit router (PE1):
show mpls ilm-table
!
! SR-MPLS data-plane reachability test to a remote loopback (PE1):
ping mpls isis-sr ipv4 10.10.100.6/32 detail
!
! EVPN BGP session state for the L2VPN EVPN family (P2 RR and PE4):
show bgp l2vpn evpn summary
!
! EVPN MPLS binding and PE-to-PE tunnel state (PE4):
show evpn mpls
show evpn mpls tunnel
!
! EVPN Type-5 IP-prefix routes received from remote PEs (PE4):
show bgp l2vpn evpn prefix-route
!
! Per-VRF MPLS forwarding table and detailed prefix entries (PE4):
show mpls vrf-forwarding-table
show mpls vrf-table
!
! VRF route table, local plus routes learned via MP-BGP (PE4):
show ip route vrf EVPN-L3VPN database
!
! End-to-end reachability from PE to remote CE over the VRF (PE4):
ping 60.60.60.60 vrf EVPN-L3VPN- EVPN-L3VPN: Single Domain
- SR-MPLS Fundamentals
- LDP to SR Migration
- OcNOS-SP Product Page
- Contacter IP Infusion
IP Infusion Engineering Team
Approfondissez. Emportez-le avec vous.
La fiche technique du produit et des téléchargements techniques et concis qui vont plus loin que cette page.
Datasheet OcNOS-SP
Spécification complète OcNOS-SP : l'ensemble des fonctionnalités access, cell site et agrégation, les SKU logiciels, les plateformes matérielles prises en charge et le guide de commande de la solution.
Obtenir la fiche technique
Mise à niveau SR-MPLS avec OcNOS
Migrez SR-MPLS vers OcNOS sur du matériel ouvert : Flex-Algo, TI-LFA et une bascule nœud par nœud.
Obtenir le brief
Transport WAN Cloud & Opérateurs
Transport WAN pour le cloud et les service provider sur du matériel ouvert : SR-MPLS, EVPN et transfert testé à l'échelle.
Obtenir le briefDatasheet OcNOS-SP
Formulaire rapide. Votre PDF s'ouvre dans un nouvel onglet immédiatement après l'envoi.
✓ Ouverture de votre PDF dans un nouvel onglet…
S'il ne s'est pas ouvert, utilisez le lien ci-dessous.
Mise à niveau SR-MPLS avec OcNOS
Formulaire rapide. Votre PDF s'ouvre dans un nouvel onglet immédiatement après l'envoi.
✓ Ouverture de votre PDF dans un nouvel onglet…
S'il ne s'est pas ouvert, utilisez le lien ci-dessous.
Transport WAN Cloud & Opérateurs
Formulaire rapide. Votre PDF s'ouvre dans un nouvel onglet immédiatement après l'envoi.
✓ Ouverture de votre PDF dans un nouvel onglet…
S'il ne s'est pas ouvert, utilisez le lien ci-dessous.