EVPN E-LAN (Ethernet LAN) is the EVPN model for multipoint Layer 2 connectivity that lets multiple customer sites share a common Ethernet broadcast domain over an MPLS/SR backbone. It is the modern replacement for VPLS, delivering the same multipoint service with better scalability, faster convergence, and native multi-homing through the BGP control plane.
EVPN-ELAN vs. VPLS
| 機能 | VPLS | EVPN E-LAN |
|---|---|---|
| MAC learning | Data plane (flooding) | BGP control plane |
| BUM traffic | Flood to all PEs | Ingress replication or multicast |
| マルチホーミング | H-VPLS (complex) | Native ESI-based |
| Fast convergence | Slow (MAC aging) | Mass withdrawal (sub-second) |
| Split-horizon | Manual configuration | Automatic via ESI |
| L3 integration | Separate L3VPN required | EVPN IRB (native) |
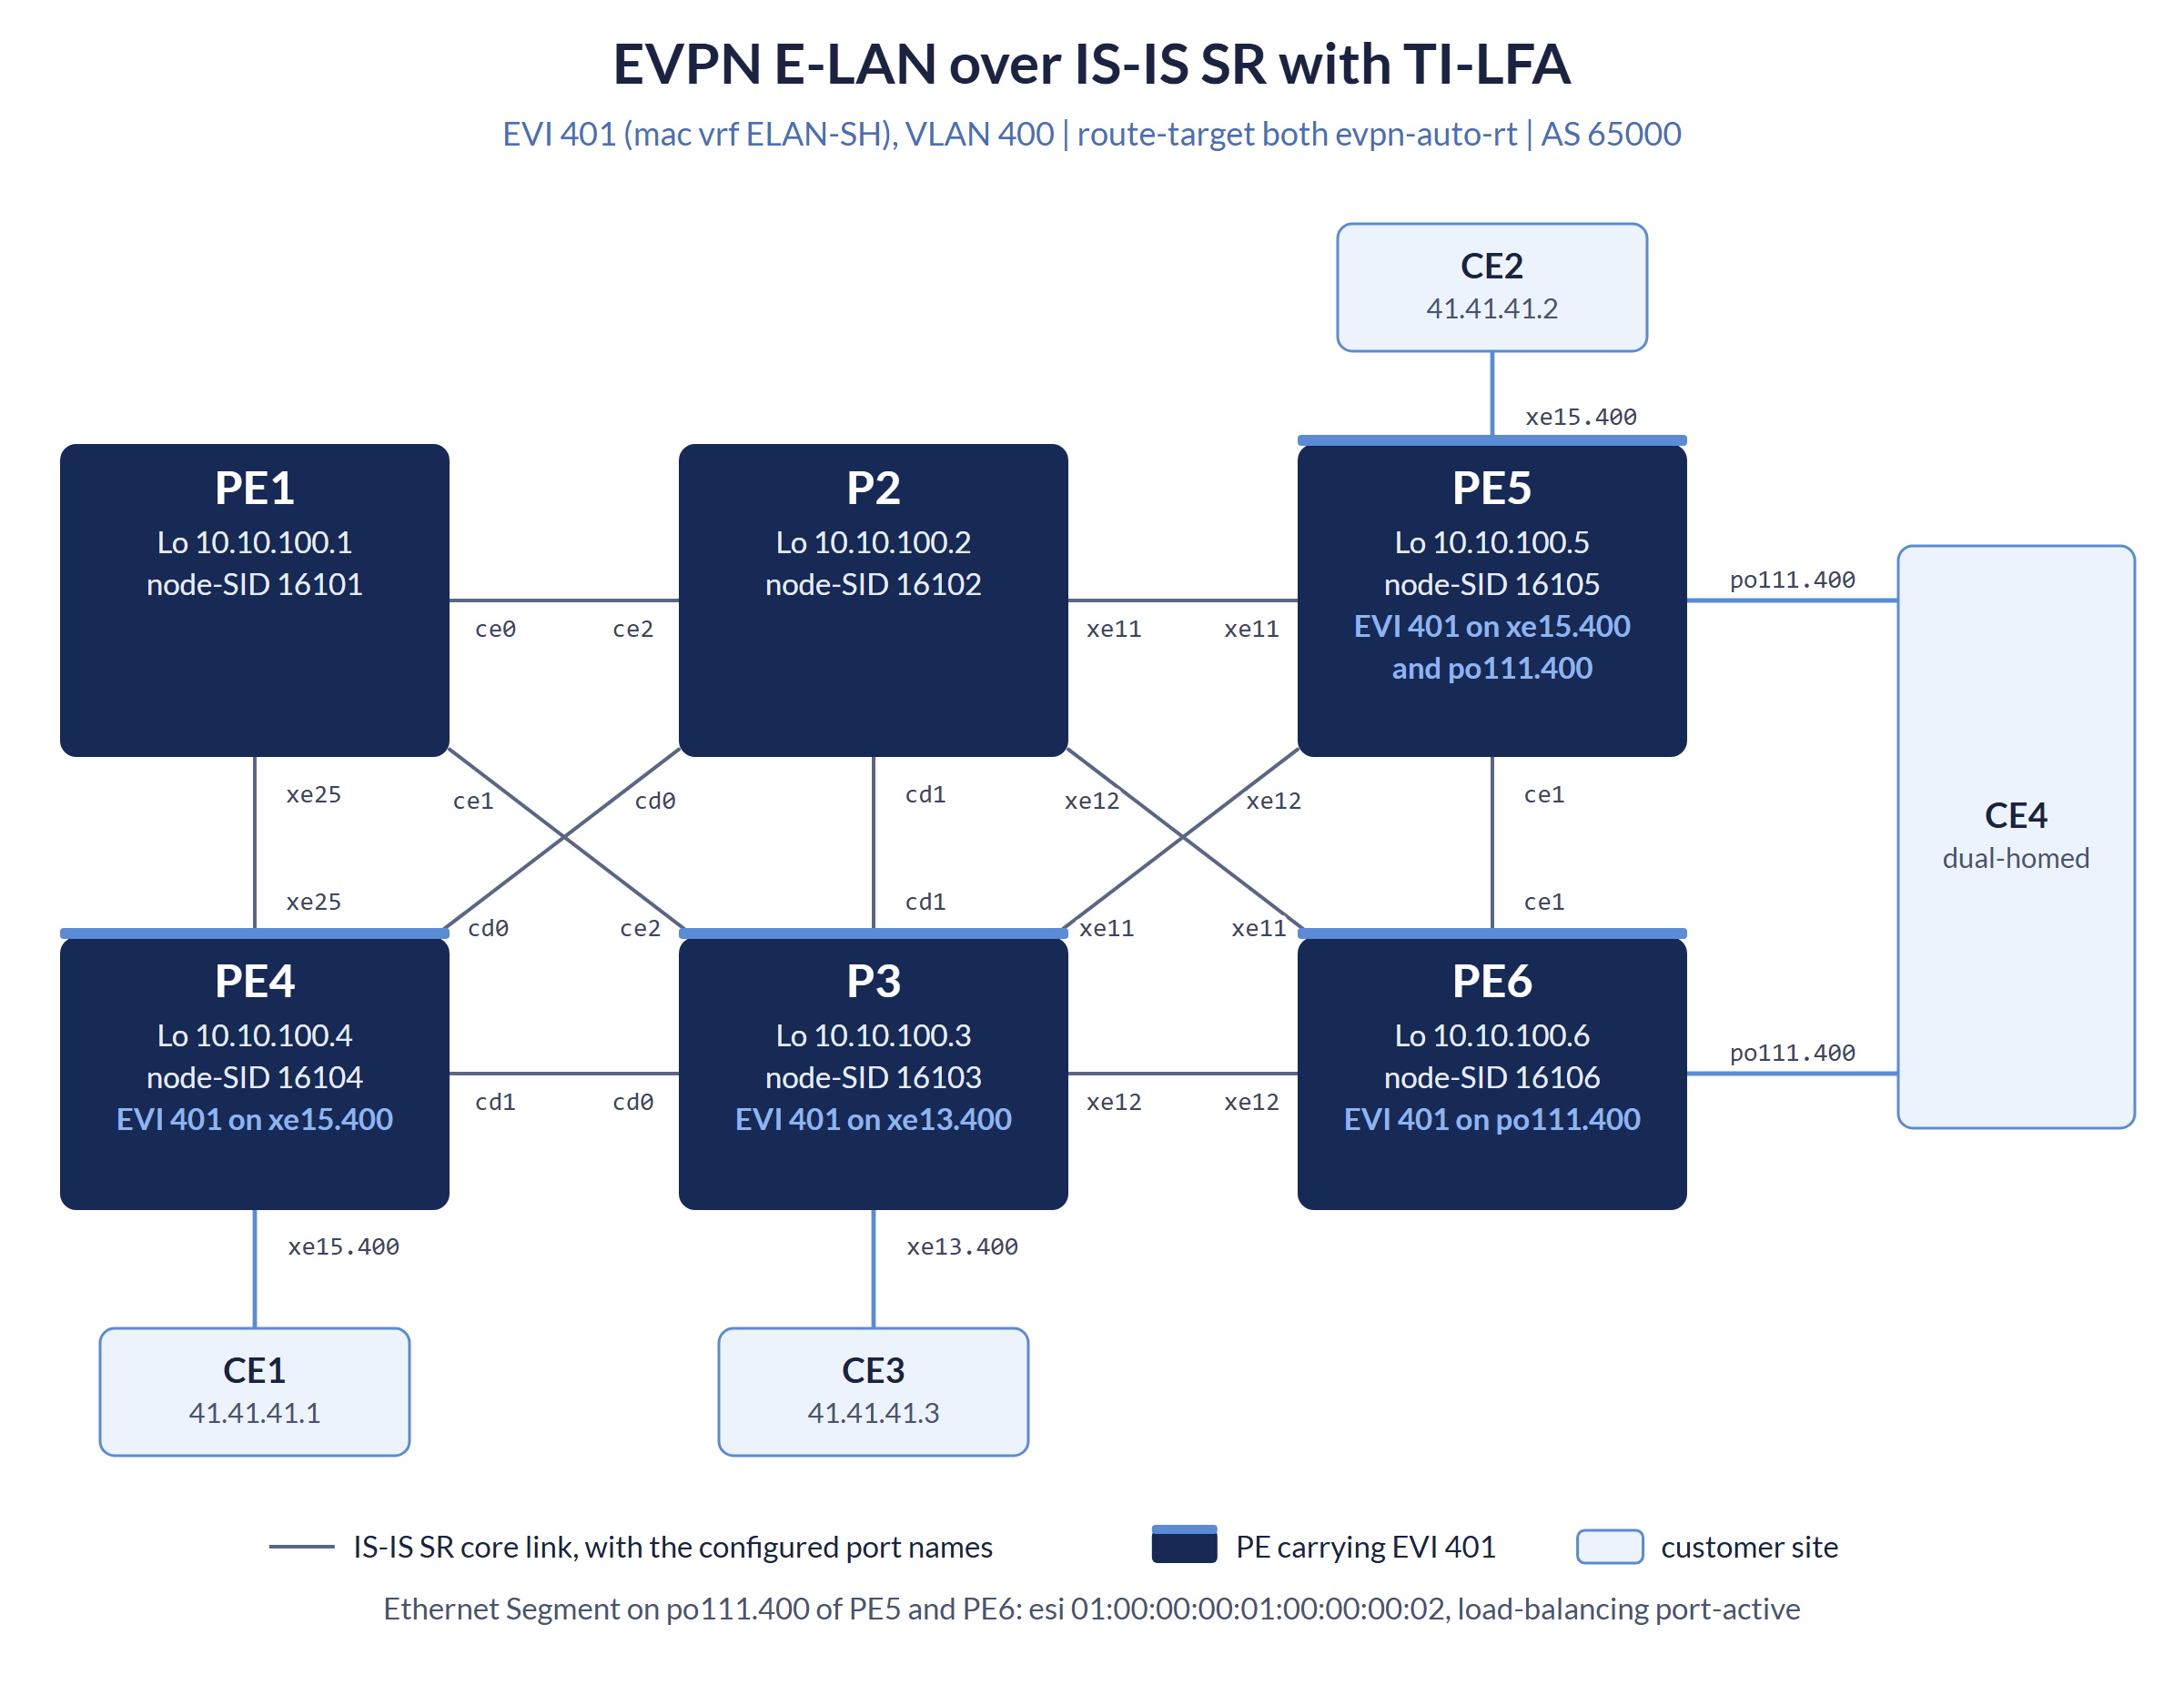
EVPN-ELAN Topology
Step 1: ISIS-SR Underlay with TI-LFA
The transport is built with IS-IS level-2-only, segment routing over MPLS, and TI-LFA for IGP fast reroute. Each PE advertises a node SID via a prefix-sid index on its loopback. The following is taken from the running configuration of PE1 (loopback 10.10.100.1).
! OcNOS PE1 - loopback with SR node SID
interface loopback1
 ip address 10.10.100.1/32
 prefix-sid index 101
!
! CE-facing / core interface (MPLS + IS-IS enabled)
interface ce0
 description To-P2-ce2
 load-interval 30
 ip address 10.66.12.1/24
 mtu 9216
 label-switching
 isis network point-to-point
 isis circuit-type level-2-only
 ip router isis OCNOS
 no isis hello padding
!
! IS-IS with segment-routing MPLS and TI-LFA
router isis OCNOS
 is-type level-2-only
 metric-style wide
 mpls traffic-eng router-id 10.10.100.1
 mpls traffic-eng level-2
 capability cspf
 dynamic-hostname
 fast-reroute ti-lfa level-2 proto ipv4
 net 49.0001.0000.0000.0001.00
 passive-interface loopback1
 segment-routing mpls
!
commitTI-LFA (fast-reroute ti-lfa level-2 proto ipv4) is an IGP segment-routing fast-reroute mechanism: it precomputes a loop-free backup path in the IS-IS SR data plane so traffic reroutes locally on link or node failure. This is distinct from EVPN mass withdrawal, which is a BGP-EVPN control-plane mechanism for fast MAC/ESI convergence. The two operate at different layers and should not be conflated.
Step 2: BGP EVPN Control Plane
The overlay uses iBGP in AS 65000 with the L2VPN EVPN address family. In this lab P2 acts as the EVPN route reflector; P3 and the PEs peer to it as clients. Route-reflector configuration from P2 (10.10.100.2):
! OcNOS P2 - EVPN route reflector
router bgp 65000
 bgp router-id 10.10.100.2
 no bgp inbound-route-filter
 neighbor EVPN-RRC peer-group
 neighbor EVPN-RRC remote-as 65000
 neighbor EVPN-RRC update-source loopback1
 neighbor 10.10.100.3 peer-group EVPN-RRC
 neighbor 10.10.100.4 peer-group EVPN-RRC
 neighbor 10.10.100.5 peer-group EVPN-RRC
 neighbor 10.10.100.6 peer-group EVPN-RRC
 !
 address-family l2vpn evpn
 neighbor EVPN-RRC activate
 neighbor EVPN-RRC route-reflector-client
 exit-address-family
 !
 exit
!
commit
Route-reflector client configuration from a PE (PE4, 10.10.100.4):
! OcNOS PE4 - EVPN route-reflector client
router bgp 65000
 bgp router-id 10.10.100.4
 neighbor 10.10.100.2 remote-as 65000
 neighbor 10.10.100.2 update-source loopback1
 !
 address-family l2vpn evpn
 neighbor 10.10.100.2 activate
 exit-address-family
 !
 exit
!
commit
Step 3: Enable EVPN-MPLS
EVPN over MPLS is enabled globally, with IRB for integrated routing and bridging, and the local VTEP anchored on the loopback address. From PE4 (10.10.100.4):
! OcNOS PE4 - global EVPN-MPLS enablement
evpn mpls enable
!
evpn mpls irb
!
evpn mpls vtep-ip-global 10.10.100.4
!
commit
Step 4: Single-Homed EVPN-ELAN Service
An E-LAN broadcast domain on OcNOS is built with a mac vrf, an evpn mpls id for the EVI, and an access-if-evpn stanza that maps the CE-facing interface into the VPN with map vpn-id. The commands below use the correct OcNOS EVPN-MPLS L2 syntax.
! OcNOS - single-homed E-LAN service (EVI 401, VLAN 400)
!
mac vrf ELAN-SH
 rd 10.10.100.4:400
 route-target both evpn-auto-rt
!
evpn mpls id 401
 host-reachability-protocol evpn-bgp ELAN-SH
!
! Attach the CE-facing interface to the E-LAN
interface xe15.400 switchport
 encapsulation dot1q 400
 access-if-evpn
  map vpn-id 401
 exit
!
commit
Step 5: Multi-Homed EVPN-ELAN Service (ESI)
For a multi-homed CE, OcNOS configures the Ethernet Segment Identifier at the interface level (on the LAG or access interface) with evpn multi-homed esi and a load-balancing mode (single-active or port-active). There is no separate evpn ethernet-segment node and no all-active keyword in this model; split-horizon and DF election follow from the shared ESI advertised in BGP-EVPN.
! OcNOS - multi-homed E-LAN service with ESI (EVI 401, VLAN 400)
!
interface po111.400 switchport
 evpn multi-homed esi 01:00:00:00:01:00:00:00:02 load-balancing port-active
 encapsulation dot1q 400
 access-if-evpn
  map vpn-id 401
 exit
!
commit
Verification
The following commands were run in the lab and confirm the SR underlay and the EVPN control plane. SR reachability and label imposition from PE1:
! OcNOS PE1 - SR underlay verification
show isis topology
show mpls forwarding-table
show mpls ilm-table
ping mpls isis-sr ipv4 10.10.100.6/32 detail
! Result: Success Rate is 100.00 percent (5/5),
! round-trip min/avg/max = 0.69/1.44/2.18 ms
EVPN session state on the route reflector (P2) and on a PE (PE4):
! OcNOS - BGP EVPN session verification
show bgp l2vpn evpn summary
! P2 (RR): 4 neighbors, 4 established sessions
!   10.10.100.3 / .4 / .5 / .6
! PE4: 1 neighbor (10.10.100.2), 1 established session- EVPN-ELINE: Point-to-Point L2 Service
- EVPN-ETREE: Rooted Multipoint
- EVPN-L3VPN over ISIS-SR
- OcNOS-SP Product Page
- IP Infusion へお問い合わせ
IP Infusion Engineering Team
さらに詳しく。資料をお持ち帰りください。
製品データシートと、このページよりもさらに踏み込んだ簡潔で技術的なダウンロード資料です。
OcNOS-SP データシート
OcNOS-SP の完全な仕様。アクセス、セルサイト、アグリゲーションの機能セット、ソフトウェア SKU、サポート対象ハードウェアプラットフォーム、ソリューション発注ガイドを収録しています。
データシートを入手OcNOS による SR-MPLS アップグレード
オープンハードウェア上の OcNOS へ SR-MPLS を移行。Flex-Algo・TI-LFA と、ノード単位の移行パスを解説します。
概要資料を入手クラウド & サービスプロバイダー WAN 伝送
open hardware上でのクラウドおよびservice provider向けWANトランスポート。SR-MPLS、EVPN、スケール検証済みのフォワーディングに対応します。
概要資料を入手OcNOS-SP データシート
簡単なフォームです。送信後すぐに PDF が新しいタブで開きます。
✓ PDF を新しいタブで開いています…
開かない場合は、下記のリンクをご利用ください。
OcNOS による SR-MPLS アップグレード
簡単なフォームです。送信後すぐに PDF が新しいタブで開きます。
✓ PDF を新しいタブで開いています…
開かない場合は、下記のリンクをご利用ください。
クラウド & サービスプロバイダー WAN 伝送
簡単なフォームです。送信後すぐに PDF が新しいタブで開きます。
✓ PDF を新しいタブで開いています…
開かない場合は、下記のリンクをご利用ください。